We’re moving onto something completely new now!
In this lesson, you will learn to login with Facebook.
Again, the same four steps apply:
- Create the app
- Create the sign-in link
- User logs in on Facebook
- Exchange code for access token
Create the app
Here are the instructions to create the app for facebook.
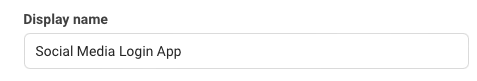
You can name the app anything you want.
- I named it Social Media Login App.
- We’re going to set
callbackURLtohttps://localhost/auth/facebook/callback.
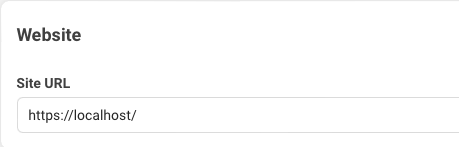
Before you move on, make sure you add your facebook credentials to the .env file.
FACEBOOK_CLIENT_ID="Your Client ID"FACEBOOK_CLIENT_SECRET="Your Client Secret"Create a sign-in link
When the user clicks the sign-in link, we will redirect the user to facebook. We can do this in two steps:
- We direct the user to an endpoint in our server.
- In this endpoint, we redirect the user to facebook.
<!-- Direct user to endpoint in our server --><a href="/auth/facebook" ...> Login with Facebook </a>In this endpoint, we craft the sign-in link for facebook.
Here are the instructions from Facebook.
If you read this page, you will notice that Facebook subtly hints that there are two required parameters — state and redirect_uri
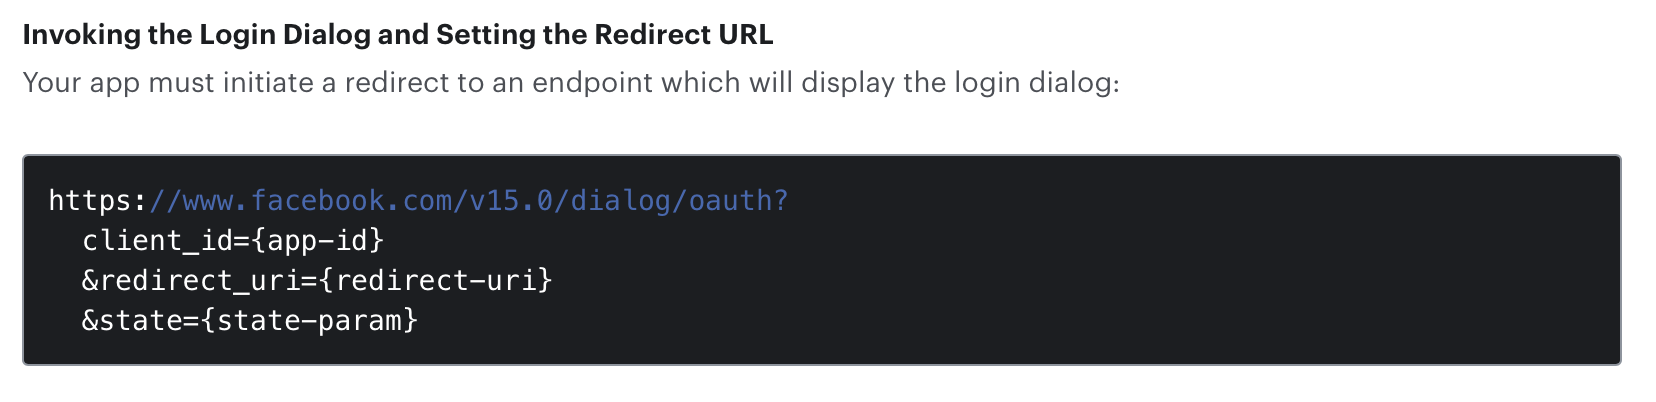
Here’s how you create the sign-in link.
router.get('/auth/facebook', async (req, res) => {  const { state } = await PKCE()  const baseURL = 'https://www.facebook.com/v15.0/dialog/oauth'  const params = {    client_id: process.env.FACEBOOK_CLIENT_ID,    redirect_uri: 'https://localhost/auth/facebook/callback',    state,  }
  const query = new URLSearchParams(params)  const link = baseURL + '?' + query.toString()})
Since Facebook requires state, we need to save state into the cookies.
router.get('/auth/facebook', async (req, res) => { // ... res.cookie('state', state, { httpsOnly: true, secure: true })})Then we redirect the user to Facebook.
router.get('/auth/facebook', async (req, res) => {  // ...
  res.redirect(link)})
User logs in to facebook
Nothing for us to do here :)
Exchange code for access token
When the user authorise the Facebook login, Facebook will redirect them back to /auth/facebook/callback.
We need to take a couple of steps here:
- Check whether
stateis valid - Grab
codefrom the url. - Send a request to facebook to get the access token
Checking whether state is valid
We need to grab both state from the callback url and state from the cookies. We’ll check whether they are the same value before we proceed with the rest of the steps.
router.get('/auth/facebook/callback', async (req, res) => {  const { state: returnedState } = req.query  const { state } = req.cookies
  if (state !== returnedState) return})
Grabbing code from the url
We need to grab code from the callback URL because we need to send it to facebook.
router.get('/auth/facebook/callback', async (req, res) => {  const { state: returnedState, code } = req.query  const { state } = req.cookies
  if (state !== returnedState) return})
Send a request to facebook
Then we send this code to Facebook’s token endpoint to get the access token.
Here are the instructions from Facebook.
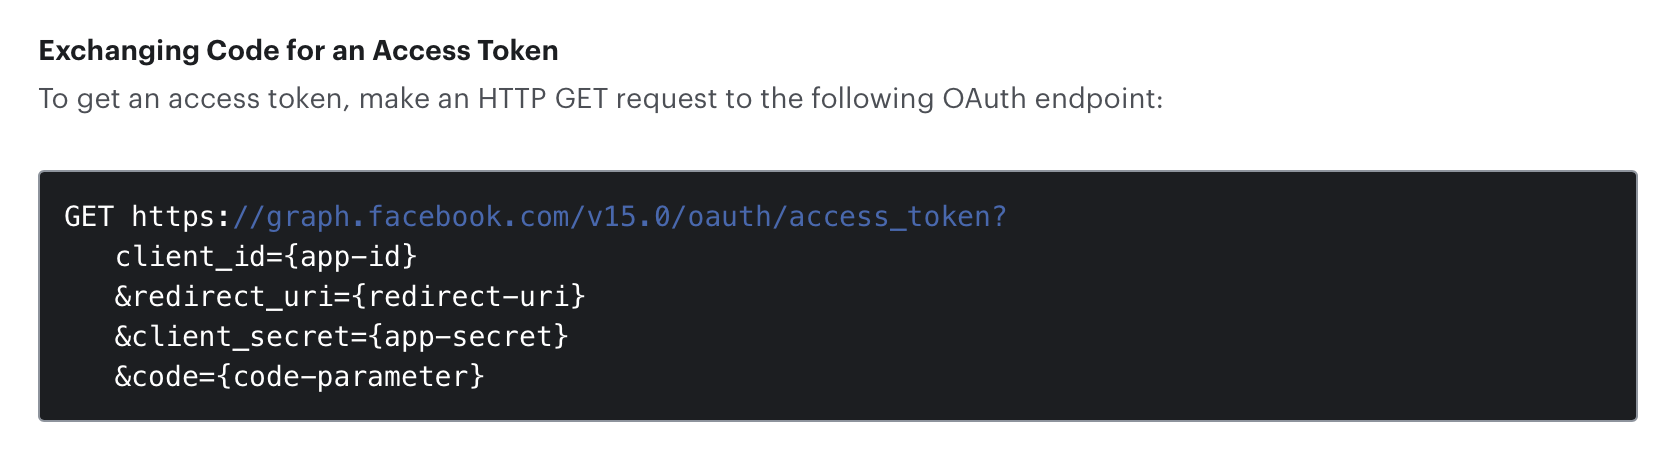
Notice two things here:
- Facebook uses a
GETrequest (while others we’ve worked on so far use aPOST) request for the endpoint. - Required parameters are
client_id,redirect_uri,client_secretandcode.
These two points means we can generate the following request:
router.get('/auth/facebook/callback', async (req, res) => {  // ...  const response = await zlFetch(    'https://graph.facebook.com/v15.0/oauth/access_token',    {      query: {        client_id: process.env.FACEBOOK_CLIENT_ID,        client_secret: process.env.FACEBOOK_CLIENT_SECRET,        redirect_uri: 'https://localhost/auth/facebook/callback',        code,      },    },  )
  const token = response.body  console.log(token)})
You should receive a token like this:
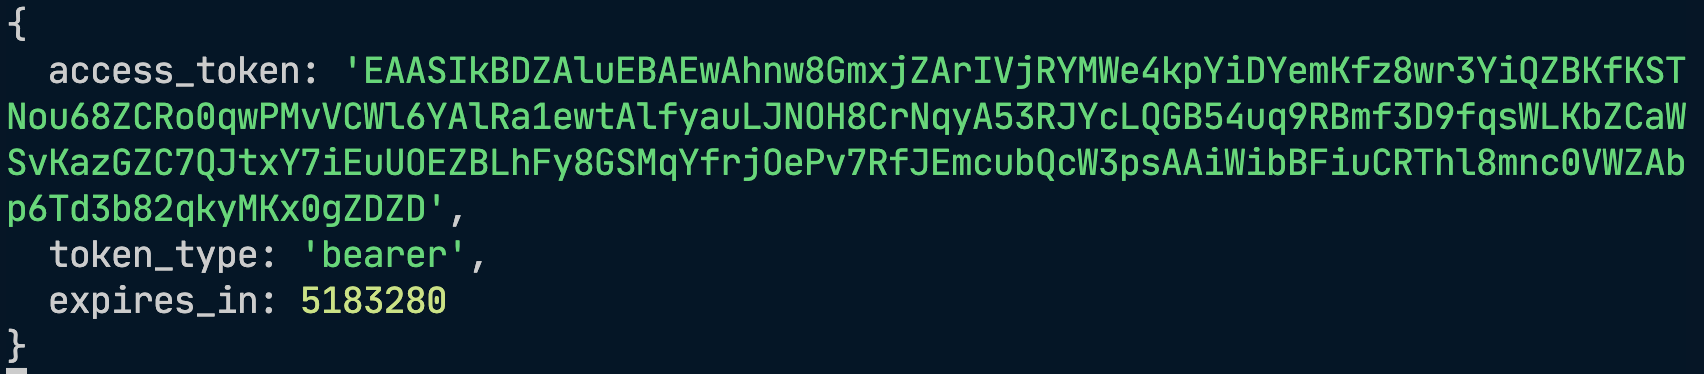
The user is now logged in.
Handling the access token
We’re going to store the access token in Local Storage in the next lesson.
Welcome! Unfortunately, you don’t have access to this lesson. To get access, please purchase the course or enroll in Magical Dev School.
Unlock this lesson