The state variable is a defense against CSRF Attacks (Cross-Site Request Forgery attacks).
The idea is — if you use a random state value, it would be impossible for others to guess this state value, so it would be impossible for them to generate a sign-in link that works on your server.
The same is true for code_verifier. If you use a random code_verifier value, it would be impossible for others to guess this code_verifier value, so code_challenge will be secure on the identity provider’s end.
So you should always generate random state and code_verifier values (unless when you’re learning how they work).
These values can be saved in cookies.
Understanding Cookies
Cookies are small pieces of data that are stored in a browser. This data is sent to the server when the browser makes a request.
Here’s what you need to know:
- Most cookies are created on the server.
- Both frontend and server can read and set cookies, but the server has more options. For example, servers can set cookies that the frontend cannot read. These cookies are used to enhance security.
Storing state and code_verifier in cookies
First, you need to point users to a route in your server.
<a class="button" href="/auth/twitter">Login with Twitter</a>Users will be directed to a route handler when they click on the login button.
In this route handler, we generate the sign-in link and redirect users to the identity provider with res.redirect.
app.get('/auth/twitter', async (req, res) => {  const baseURL = 'https://twitter.com/i/oauth2/authorize'  const params = {    /* ... */  }  const query = new URLSearchParams(params)  const link = baseURL + '?' + query.toString()
  res.redirect(link)})
From a user’s point of view, they won’t know they went to our server, because the next thing they see is the identity provider’s login page.
Before we redirect users to the identity provider, we can save the state and code_verifier values in cookies. We do this with res.cookie.
router.get('/auth/twitter', async (req, res) => {  // ...
  res.cookie('state', state)  res.cookie('code_verifier', code_verifier)
  res.redirect(link)})
I recommend adding two more cookie attributes as you set the cookie.
httpOnly— ensures browsers cannot view this cookie, which ensures that the cookie value will not be stolen even if someone had access to your frontend JavaScript.secure— ensures cookies are sent only in a HTTPS scheme, which ensures the cookies will not be intercepted in the middle of the request. (This attribute is not required if you already use HTTPS).
router.get('/auth/twitter', async (req, res) => {  // ...
  res.cookie('state', state, {    httpOnly: true,    secure: true,  })  res.cookie('code_verifier', code_verifier, {    httpOnly: true,    secure: true,  })
  res.redirect(link)})
Getting state and code_verifier from cookies
When you receive a response from the callbackURL, you can check the cookies for state and code_verifier values.
router.get('/auth/twitter/callback', async (req, res) => { const { state, code_verifier } = req.cookies console.log(state) console.log(code_verifier)})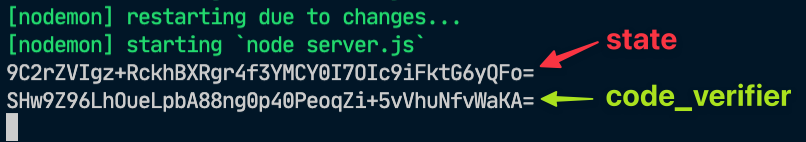
We want to check whether the state value stored in the cookie is the same as the state value returned from the identity provider. If both values are the same, we know we’re safe from CSRF attacks.
router.get('/auth/twitter/callback', async (req, res) => {  const { state, code_verifier } = req.cookies  const { state: returnedState, code } = req.query
  if (state !== returnedState) return})
From this point on, you can use code and code_verifier to exchange for an access token.
router.get('/auth/twitter/callback', async (req, res) => { // ... const response = await zlFetch.post('...', { body: { code, code_verifier, // Other values you need to get an access token }, })})That’s it.
Welcome! Unfortunately, you don’t have access to this lesson. To get access, please purchase the course or enroll in Magical Dev School.
Unlock this lesson